VLANs and Guest Network Separation in Hotels: Design, Configuration and Testing Guide
In short: what is a VLAN and why do hotels use it?
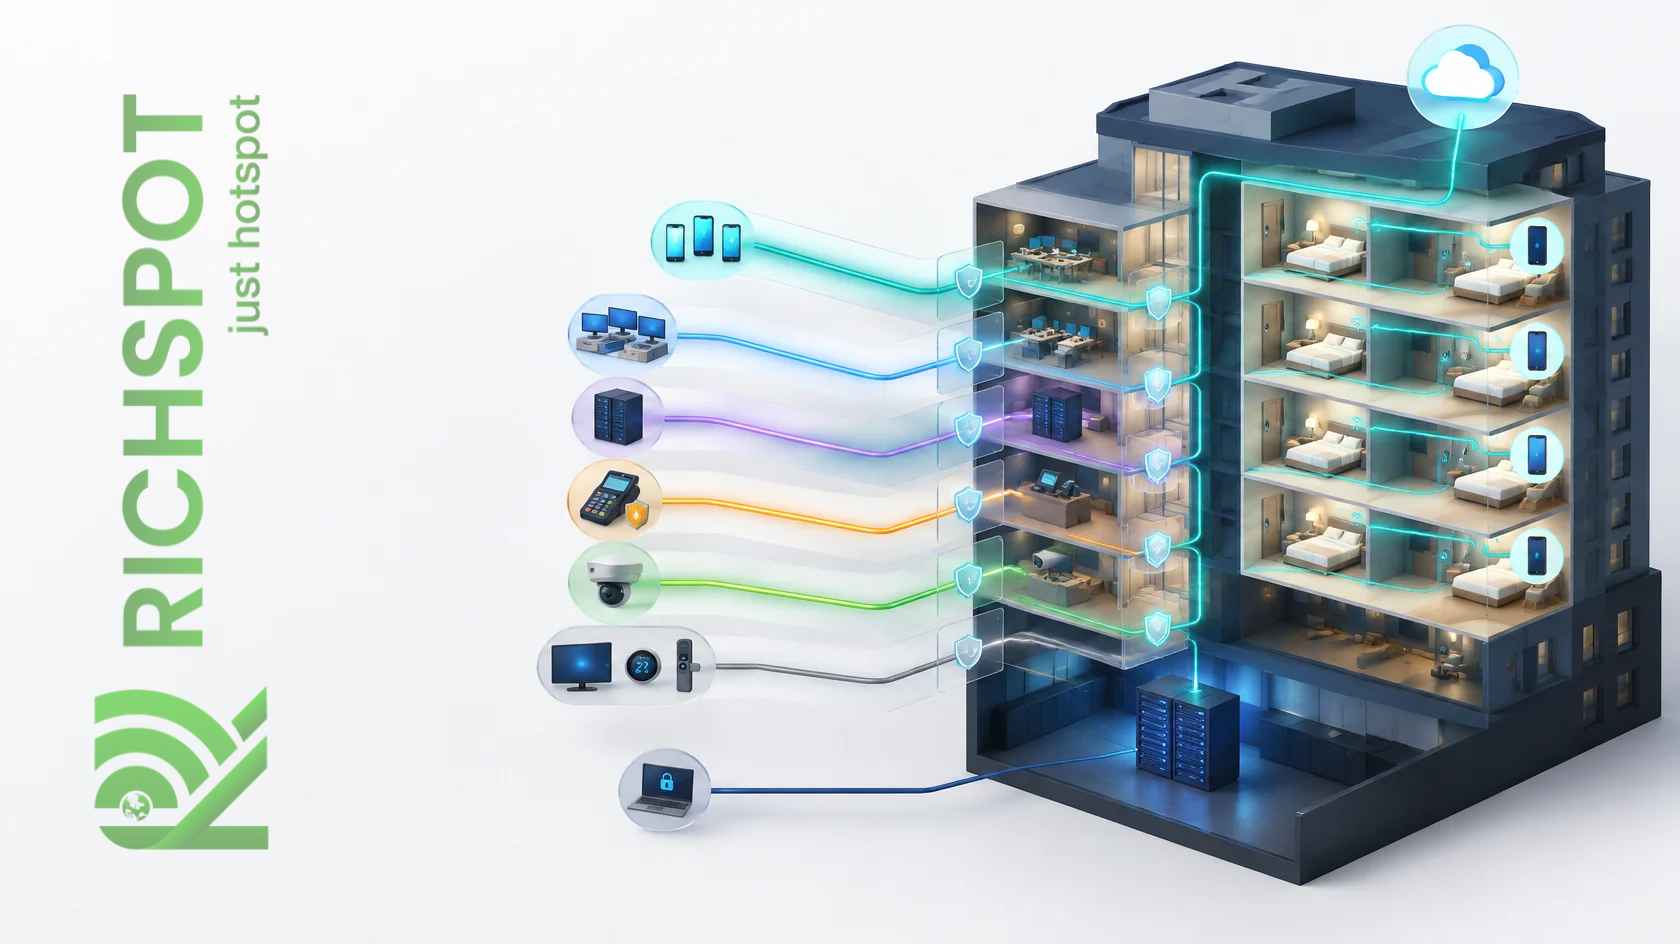
A VLAN (Virtual Local Area Network) is a technology that allows several logically isolated networks to be created on the same physical cabling and switch infrastructure. In hotels, VLANs are used to separate device groups such as guest Wi-Fi, staff computers, POS terminals, camera systems, IPTV, building automation and network management. This separation simplifies access control, limits the impact of a security incident, reduces broadcast traffic and speeds up troubleshooting. However, a VLAN does not provide full security on its own; traffic between VLANs must be controlled with firewall rules.
What does a hotel network look like without VLANs?
In a hotel network without VLANs, all devices are on the same "flat" network. A guest's phone, the reception computer, the accounting server, the POS device at the till, the security camera recorder and smart TVs all get addresses from the same IP block and can see each other directly. The consequences of this setup are:
- A guest device infected with malware can scan the hotel's computers.
- The management interface of the camera recorder or printer becomes reachable from the guest network.
- Broadcast traffic spreads across the whole network; performance drops as the network grows.
- When a problem occurs, it is hard to find which device group it comes from.
- Applying different policies (speed, access, logging) to different device groups is almost impossible.
With VLANs, each device group runs in its own logical network, and communication between groups is possible only through explicitly permitted rules.
Key concepts
VLAN ID
Each VLAN is identified by a number between 1 and 4094 — for example 10 for the guest network and 20 for the staff network.
Tagging (802.1Q)
To carry several VLANs over the same cable, a tag indicating the VLAN number is added to Ethernet frames. This standard is known as IEEE 802.1Q.
Access port
A switch port that belongs to a single VLAN and carries untagged traffic. VLAN-unaware devices such as computers, printers or cameras are connected to access ports. For example, the port the reception computer is connected to is assigned to VLAN 20 as an access port.
Trunk port
A port that carries several VLANs tagged. Links between switches, the router connection and access points broadcasting several SSIDs are usually connected to trunk ports.
Native / untagged VLAN
The VLAN to which untagged traffic arriving on a trunk port is assigned. For security, it is recommended to set the native VLAN to an unused VLAN or manage it carefully.
Inter-VLAN routing
Routing traffic between different VLANs via a router or layer 3 switch. This is where firewall rules come in and determine which VLAN can reach which.
Example hotel VLAN plan
An example plan for a mid-sized hotel:
- VLAN 10 – Guest Wi-Fi: 10.10.0.0/22 – Hotspot active, internet access only
- VLAN 20 – Staff: 10.20.0.0/24 – Office computers, staff Wi-Fi
- VLAN 30 – Hotel systems: 10.30.0.0/24 – PMS server, accounting, file server
- VLAN 40 – POS: 10.40.0.0/24 – Tills and payment terminals
- VLAN 50 – Cameras: 10.50.0.0/24 – IP cameras and recorder
- VLAN 60 – IPTV and IoT: 10.60.0.0/24 – Room TVs, smart thermostats, door locks
- VLAN 99 – Management: 10.99.0.0/24 – Switch, access point and router management interfaces
For each VLAN, the gateway address, DHCP pool, DNS server and lease time should be defined separately. On the guest network, the subnet should be large enough for peak-season capacity and the lease time kept short.
Inter-VLAN access matrix
The most important output of VLAN design is an access matrix showing which network may reach which. The basic principle should be "block by default, open what is needed":
- Guests → Internet: Allow
- Guests → All other VLANs: Block
- Staff → Hotel systems: Required ports only
- Staff → Internet: Allow (filtered if needed)
- POS → Payment provider addresses: Required destinations only
- POS → Other VLANs: Block
- Cameras → Recorder: Allow; block internet access if not needed
- IoT → Manufacturer cloud services: Required destinations only
- Management → All network devices: Allow (only from authorised administrator devices)
- Any VLAN → Management: Block
This matrix should be put in writing and implemented exactly with firewall rules.
VLANs on the wireless network
Modern access points can broadcast several SSIDs and map each SSID to a different VLAN. For example:
- "Hotel-Guest" SSID → VLAN 10
- "Hotel-Staff" SSID → VLAN 20 (WPA2/WPA3-Enterprise)
- "Hotel-IoT" SSID (hidden) → VLAN 60
In this setup, the switch port to which the access point is connected is configured as a trunk and the relevant VLANs are carried tagged. The access point's own management address is kept in the management VLAN. Client isolation must be enabled on the guest SSID.
Example configuration: MikroTik (RouterOS v7)
The example below shows how to define guest and staff VLANs on a MikroTik router with bridge VLAN filtering and isolate the guest network from other networks. Interface names and addresses are examples.
/interface bridge add name=br-lan vlan-filtering=yes
/interface bridge port add bridge=br-lan interface=ether2 comment="Core switch trunk"
/interface bridge port add bridge=br-lan interface=ether5 pvid=20 comment="Reception PC access"
/interface bridge vlan add bridge=br-lan tagged=br-lan,ether2 vlan-ids=10,20,30,99
/interface bridge vlan add bridge=br-lan tagged=br-lan untagged=ether5 vlan-ids=20

/interface vlan add interface=br-lan name=vlan10-guest vlan-id=10
/interface vlan add interface=br-lan name=vlan20-staff vlan-id=20
/interface vlan add interface=br-lan name=vlan30-systems vlan-id=30

/ip address add address=10.10.0.1/22 interface=vlan10-guest
/ip address add address=10.20.0.1/24 interface=vlan20-staff
/ip address add address=10.30.0.1/24 interface=vlan30-systems

# Readable firewall with interface lists
/interface list add name=LAN-INTERNAL
/interface list member add list=LAN-INTERNAL interface=vlan20-staff
/interface list member add list=LAN-INTERNAL interface=vlan30-systems
/ip firewall filter add chain=forward in-interface=vlan10-guest out-interface-list=LAN-INTERNAL action=drop comment="Guest -> internal blocked"
In a real installation, in addition to these rules, only the required ports should be opened from the staff network to hotel systems, access to the management VLAN should be restricted and rule order should be compatible with the hotspot's dynamic rules.
Test steps
After configuring VLANs, the following tests must be carried out:
- Confirm that internet access works from a device on the guest network.
- From the same device, try pinging and connecting to addresses on the staff network, hotel systems, POS and management network; confirm that all are blocked.
- Check that two devices on the guest network cannot reach each other (client isolation).
- Confirm that a staff device can reach only the permitted servers and ports.
- Check that DHCP hands out addresses from the correct pool on each VLAN.
- Test that each SSID on the access points lands on the correct VLAN.
- Verify port by port that switch ports have the correct access/trunk settings.
- Confirm that management interfaces are reachable only from the management VLAN.
Migration plan from a flat network to VLANs
Rebuilding the network of an operating hotel overnight can be risky. A gradual migration plan minimises the risk of outages:
- Take inventory: List all devices on the network (computers, POS, cameras, printers, TVs, access points, switches) and the ports they are connected to. Note devices with static IPs in particular.
- Write the plan: Document VLAN numbers, IP blocks, DHCP pools and the access matrix.
- Create the management network first: Move the management addresses of switches and access points to the management VLAN so that you do not lose access to devices in later steps.
- Separate the guest network: The quickest security gain is separating the guest network. Map the guest SSID to VLAN 10 and apply hotspot and firewall rules.
- Move critical systems: Move POS, cameras and hotel systems one at a time to their own VLANs. After each move, test that the relevant application works.
- Organise the staff network: Move staff computers and staff Wi-Fi to VLAN 20 and open only the required access to servers.
- Final check and clean-up: Shut down unused ports, remove old rules and document the final state.
Each step should be carried out during low-occupancy hours with a rollback plan.
Example scenario: what happens without separation?
Imagine a hotel using a flat network where malware on a guest's laptop scans other devices on the network. Within a short time it finds the reception computers, shared folders and a camera recorder left with its default password. As a result, hotel data is put at risk and finding the source of the incident takes days. Had VLANs and firewall rules been in place at the same hotel, the infected device could only have reached the internet and would not even have seen other guest devices; the impact would have been limited to a single guest device.
Common mistakes
- !Wrong port assignment: A POS device accidentally connected to a port assigned to the guest VLAN.
- !Missing trunk setting: The guest VLAN not defined as tagged on the access point's port, so guests cannot get an IP address.
- !VLANs without a firewall: Defining VLANs but leaving traffic between them unrestricted on the router.
- !DHCP conflicts: More than one DHCP server handing out addresses on the same VLAN.
- !Neglecting the native VLAN: Untagged traffic landing on an unexpected VLAN.
- !Lack of documentation: Not recording which port belongs to which VLAN prolongs troubleshooting by hours.
- !Leaving the management network open: Switch and access point management interfaces reachable from the guest network.
Measures to apply together with VLANs
A VLAN is a beginning, not an end. For a secure hotel network, the following should be applied alongside VLANs:
- Inter-VLAN firewall rules and an access matrix
- Client isolation on the guest network
- Captive portal-based user authentication
- Strong administrator passwords and up-to-date software on network devices
- Shutting down unused switch ports
- Central logging and monitoring
Frequently asked questions
Do I need to buy new switches for VLANs?
VLANs require managed (or smart) switches. Unmanaged switches do not understand VLAN tags and cannot separate traffic. Whether your existing switches support VLANs should be checked model by model.
How many VLANs should I use?
Too many VLANs make management harder, while too few bundle risks together. For most hotels, five to seven VLANs — guests, staff, hotel systems, POS, cameras, IoT and management — is a balanced starting point.
Do VLANs affect internet speed?
VLAN tagging has a negligible effect on performance. On the contrary, because it reduces broadcast traffic and separates traffic, it can have a positive effect on performance in large networks.
Can guest Wi-Fi and staff Wi-Fi be broadcast from the same access point?
Yes. If the access point can map each SSID to a different VLAN, the two networks can be broadcast from the same hardware while remaining completely separate logically.
Is a separate VLAN needed for IPTV and smart room devices?
It is recommended. Smart TVs, thermostats, door locks and similar IoT devices often have limited security features and may not receive updates for long periods. Keeping these devices on a separate VLAN prevents a potential vulnerability from spreading to the guest network or hotel systems. Services that use multicast, such as IPTV, are also easier to manage on a separate network.
Who should configure VLANs?
Network design and configuration should be done and documented by an experienced network specialist. Because a wrong trunk or firewall setting can cut off connectivity for the whole hotel, changes should be made during a maintenance window with a rollback plan.
Next step with Richspot
Richspot Hotspot provides the captive portal, user authentication, session and bandwidth management and logging layer within the scope of Law No. 5651, running on the guest VLAN. Thanks to its structure optimised for MikroTik RouterOS, it can be positioned as the guest access layer in VLAN-based network architectures.
Determine how Richspot Hotspot will fit into your existing VLAN and MikroTik architecture during project design. Evaluate your network structure together with the expert team.
